
• Home
  • About us
  • Services

    Business Support

    • Monitoring and Maintenance
    • Business Continuity
    • Remote Support
    • IT Support
    • Cloud Computing
    • AI Workflows Reviews

    Cyber Security

    • CISSP Gold Coast
    • Netlogyx Threat Locker
    • Office 365 Backup
    • Penetration Testing
    • Security Awareness Training
    • Sentinelone
    • SIEM
    • Vulnerability Management
    • Soc 2 Compliance
    • Business Cyber Security Policies
    • CrowdStrike Ultimate Protection Suite
    • Google Workspace Audit
    • Microsoft 365 Audit

    Useful Links

    • Shop.netlogyxit.com.au
    • Refurbished Hardware
    • Office 365
    • Remote Working Support
  • Pricing
  • Blog
  • Free IT Guides
  • Support
  • Shop
  • Home
  • About us
  • Services

    Business Support

    • Monitoring and Maintenance
    • Business Continuity
    • Remote Support
    • IT Support
    • Cloud Computing
    • AI Workflows Reviews

    Cyber Security

    • CISSP Gold Coast
    • Netlogyx Threat Locker
    • Office 365 Backup
    • Penetration Testing
    • Security Awareness Training
    • Sentinelone
    • SIEM
    • Vulnerability Management
    • Soc 2 Compliance
    • Business Cyber Security Policies
    • CrowdStrike Ultimate Protection Suite
    • Google Workspace Audit
    • Microsoft 365 Audit

    Useful Links

    • Shop.netlogyxit.com.au
    • Refurbished Hardware
    • Office 365
    • Remote Working Support
  • Pricing
  • Blog
  • Free IT Guides
  • Support
  • Shop
Help Me

CALL NOW: 1300044320

  • About Us
  • Services
  • Help & FAQs
  • Contact
  • Terms
  • Privacy
  • About Us
  • Services
  • Help & FAQs
  • Contact
  • Terms
  • Privacy

MFA Fatigue Attacks: The Trick That Is Bypassing Your Business Login Security

  • Home
  • Blog Details
  • June 8 2026
  • Neil Frick

Multi-factor authentication was supposed to be the answer. And for years, it was enough to stop most attackers cold. But cybercriminals adapt fast – and they have found a devastatingly simple way around MFA that does not require any technical skill whatsoever. It is called an MFA fatigue attack, and it has already been used to breach major organisations including Uber, Microsoft, and Okta. For Australian small businesses, understanding this attack is urgent – because the tools to stop it are already available, and the cost of being unprepared is significant.
Book a Consultation

What Is an MFA Fatigue Attack?

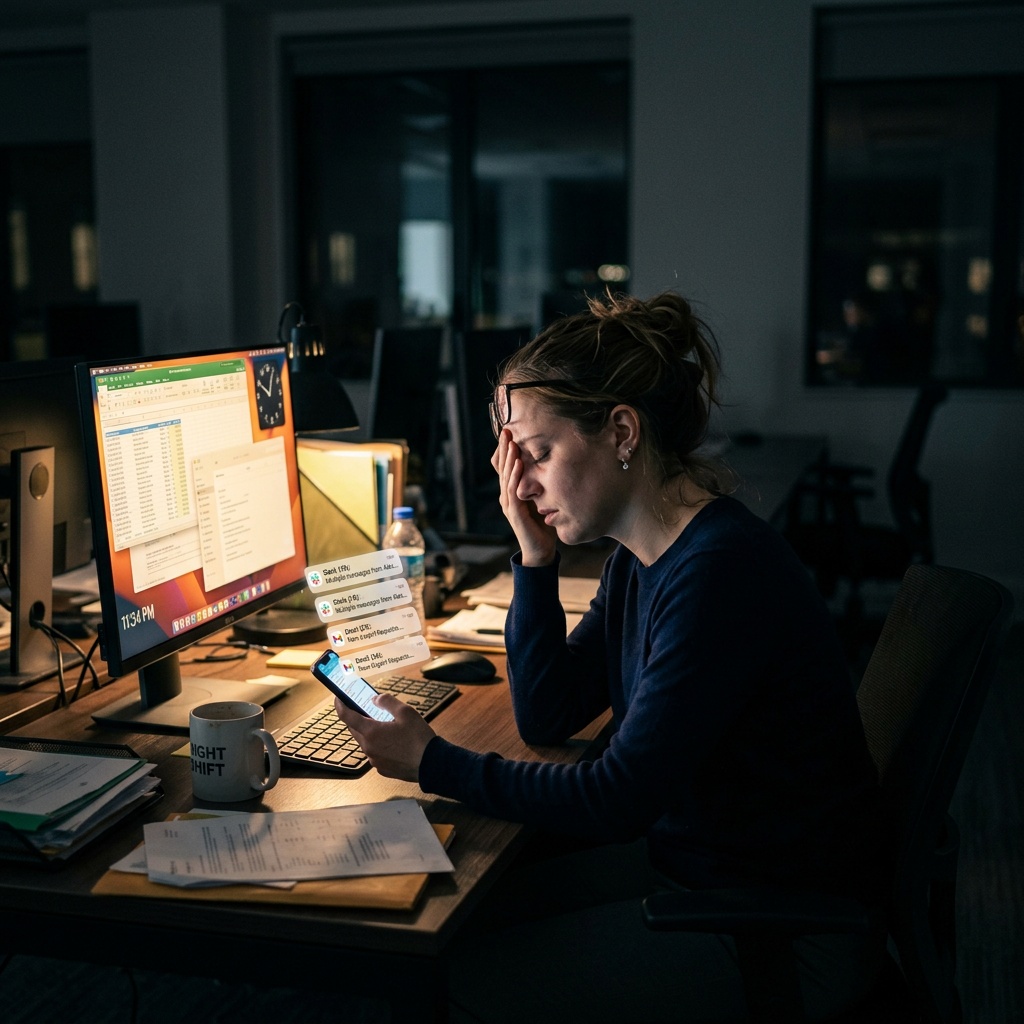
An MFA fatigue attack – also called MFA push bombing – is a social engineering technique where an attacker who already has a victim’s username and password floods their phone with repeated authentication push notifications.

The goal is simple: annoy or confuse the target into approving a login they did not initiate.

Here is how it unfolds:

  1. Attacker obtains credentials via phishing or a data breach
  2. Attacker repeatedly attempts login, triggering MFA push requests to the victim’s phone
  3. Victim receives dozens of approval prompts – often in the middle of the night
  4. Victim, confused or exhausted, taps “Approve” just to make it stop
  5. Attacker is in

Some attackers pair this with a phone call pretending to be from IT support, creating urgency and accelerating the approval. The entire attack requires zero technical exploitation on the attacker’s part.

Learn how Netlogyx Security Awareness Training protects your staff

Why MFA Fatigue Attacks Are So Effective Against SMBs

Most small and medium businesses have deployed basic MFA – often the simple “approve/deny” push notification style. While this is far better than no MFA, it creates the exact vulnerability that MFA fatigue exploits.

The reasons SMBs are particularly exposed:

  • No number matching: Staff approve pushes without verifying a code matches what they see on screen
  • No security awareness training: Employees do not know this attack exists
  • No anomaly detection: Nobody is monitoring for repeated failed logins followed by an approval from an unusual location
  • After-hours attacks: Attackers time their push flood for 2am when staff are asleep and less alert

The MFA fatigue attack works because it exploits human psychology, not technical vulnerabilities.


How to Protect Your Business Against MFA Fatigue

The good news is that this attack is entirely preventable. Here is what Netlogyx recommends:

1. Switch to Number Matching MFA
Authenticator apps like Microsoft Authenticator now support number matching – the app shows a number that must match what appears on the login screen. This stops blind approvals dead.

2. Enable Additional Context in Push Notifications
Show the user the geographic location and the device making the request. An approval prompt showing “Login attempt from Romania” is much harder to accidentally approve.

3. Move to Phishing-Resistant MFA
FIDO2 hardware keys (like YubiKeys) or passkeys are the gold standard. They cannot be intercepted, bypassed, or bombed.

4. Implement Conditional Access Policies
Block login attempts from unexpected countries, unusual devices, or outside of business hours where possible.

5. Train Your Staff
Employees should know to never approve an MFA request they did not initiate – and to immediately call IT support if they receive unexpected push notifications.

Explore our Vulnerability Management service to identify credential exposure risks


The Broader Picture: Credential Security in 2026

MFA fatigue attacks are one part of a broader credential security problem. Billions of username and password combinations are available for sale on the dark web right now. Attackers can automate credential stuffing attacks at scale – trying stolen logins against your Microsoft 365, Google Workspace, or accounting software with no effort.

The ACSC’s Essential Eight framework recommends implementing phishing-resistant MFA as a priority control for all Australian businesses. This is not bureaucratic box-ticking – it is the direct response to the attack methods being used against Australian businesses today.

Read about our Managed IT Support and security posture management

Is Your MFA Implementation Actually Protecting You?

Basic push approval MFA is no longer enough. Netlogyx can audit your current authentication setup, identify exposure to MFA fatigue attacks, and upgrade your controls to phishing-resistant methods — without disrupting your team.

Book a Consultation
  • Review your current MFA configuration across all platforms
  • Upgrade to number matching and additional context notifications
  • Train your staff on recognising and responding to MFA push flooding

Frequently Asked Questions

Q: We already have MFA set up. Are we protected from MFA fatigue attacks?
A: Not necessarily. If you are using simple push notification approval without number matching or additional context, you remain vulnerable. The type of MFA matters as much as having it in the first place.

Q: What is the most secure form of MFA for a small business?
A: FIDO2 hardware security keys are the gold standard and are completely immune to MFA fatigue and phishing. For businesses not ready for hardware keys, number matching combined with contextual push notifications is a strong step forward.

Q: How do I know if my accounts are being targeted?
A: Unexpected MFA push notifications are the clearest warning sign. Staff should be instructed to report these immediately. Monitoring sign-in logs for repeated failed attempts is also essential.


Do Not Let a Tired Employee Be Your Weakest Link

MFA fatigue attacks are a reminder that technology alone does not create security. People are always part of the equation – and attackers know it. The solution is not to blame your staff. It is to give them better tools and better training so that approving a malicious login becomes impossible, not just unlikely.

Netlogyx keeps Australian SMBs ahead of exactly these kinds of evolving threats.

(We are not looking to replace your current provider, just offering an alternative perspective)

Book a Consultation

Written by Neil Frick


Sources & References

  1. ACSC Essential Eight – https://www.cyber.gov.au/resources-business-and-government/essential-cyber-security/essential-eight
  2. Microsoft Guidance on MFA Fatigue – https://learn.microsoft.com/en-us/azure/active-directory/authentication/how-to-mfa-number-match
  3. CISA MFA Best Practices – https://www.cisa.gov/sites/default/files/publications/fact-sheet-implementing-phishing-resistant-mfa-508c.pdf

Tags ACSC Essential Eightcredential securitycybersecurity SMBFIDO2managed IT Gold CoastMFA fatigue attackmulti-factor authenticationphishing-resistant MFApush bombingUber breach
Previous Post
Zero Trust Security: Why Australian SMBs Can No Longer Trust Their Own Network
Next Post
MDR vs Antivirus: Why Your Old Security Software Is No Longer Enough

Recent Posts

  • Cybersecurity Training for Teams: Essential in Gold Coast
  • Are Your Firewalls Enough? Gold Coast SMB Insights
  • How to Secure Your Gold Coast Business
  • Understanding Cybersecurity Legislation for Gold Coast SMBs
  • Cyber Hygiene: Essential Practices for Gold Coast SMBs

Archives

  • October 2026
  • September 2026
  • August 2026
  • July 2026
  • June 2026
  • May 2026
  • April 2026
  • March 2026
  • September 2025
  • August 2025
  • July 2025
  • June 2025
  • January 2025
  • December 2024
  • November 2024
  • August 2024
  • June 2024
  • April 2024
  • March 2024
  • February 2024
  • January 2024
  • December 2023
  • November 2023
  • October 2023
  • September 2023
  • August 2023
  • July 2023
  • June 2023
  • May 2023
  • April 2023
  • March 2023
  • February 2023
  • January 2023
  • December 2022
  • November 2022
  • September 2022
  • August 2022
  • July 2022
  • June 2022
  • May 2022
  • April 2022
  • March 2022
  • December 2021
  • November 2021
  • October 2021
  • September 2021
  • August 2021
  • July 2021
  • June 2021
  • May 2021
  • April 2021
  • March 2021
  • February 2021
  • January 2021
  • December 2020
  • November 2020
  • October 2020
  • September 2020
  • August 2020
  • March 2020
  • February 2020
  • January 2020
  • December 2019
  • November 2019
  • October 2019
  • September 2019
  • July 2019
  • June 2019
  • May 2019
  • April 2019
  • March 2019
  • February 2019
  • January 2019
  • December 2018
  • November 2018
  • October 2018
  • September 2018
  • August 2018
  • July 2018
  • June 2018
  • May 2018
  • April 2018
  • March 2018
  • February 2018
  • January 2018
  • December 2017
  • November 2017
  • October 2017
  • September 2017
  • March 2017
  • November 2016
  • October 2016
  • March 2015
  • February 2015
  • January 2015
  • December 2014
  • November 2014
  • September 2014
  • August 2014

Categories

  • Business Continuity 26
  • Business Protection 21
  • Business Risk Management 16
  • Business Security 51
  • Business Technology 3
  • CISSP 2
  • Cloud Computing 9
  • Cloud Security 3
  • Compliance 9
  • Computer Repair 11
  • Cyber Security 130
  • CyberSecurity 38
  • dark web monitoring 1
  • data backup disaster recovery, 3-2-1 backup rule, RTO RPO, Microsoft 365 backup, business continuity Australia, ransomware backup, managed IT Gold Coast, SMB data protection, cloud backup Australia 1
  • Data Breaches 7
  • Defence Industry 1
  • Desktop Support Service 3
  • Education 2
  • Email Security 5
  • Firewall 2
  • Healthcare IT 1
  • IT Services 27
  • IT Solutions 16
  • IT Support 54
  • Legal and Regulatory 3
  • Managed IT Services 22
  • Managed Services 17
  • Manufacturing 1
  • Network Security Audit 22
  • OT Security 1
  • Products and Services 1
  • Risk Management 9
  • Security 12
  • Security Training 7
  • SMB Security 38
  • SOC 2 compliance 2
  • Supply Chain Security 4
  • Technology 1
  • Uncategorized 19

Tags

ACSC ACSC Essential Eight antivirus ASD Essential Eight business continuity business email compromise Business Risk Management CEO fraud cloud security credential security credential stuffing CrowdStrike Falcon Complete CrowdStrike MDR cyber incident response cyber insurance cyber risk management Cybersecurity cybersecurity awareness training cybersecurity framework Australia cybersecurity Gold Coast Brisbane cybersecurity SMB dark web monitoring data breach DMARC endpoint security Australia Essential Eight Essential Eight compliance Falcon Discover Falcon Spotlight Gold Coast IT Gold Coast IT security IT hygiene managed detection response Australia managed IT Gold Coast MFA MFA Australia Microsoft 365 backup multi-factor authentication network security outsourced IT department patch management phishing-resistant MFA SMB cybersecurity vendor risk vulnerability management SMB
We will always explain to you the problem and how it impacts your business, possible fixes and our recommendation.

Business Support

  • Monitoring and Maintenance
  • Business Continuity
  • Remote Support
  • IT Support
  • Cloud Computing

Cyber Security

  • CISSP Gold Coast
  • Netlogyx Threat Locker
  • Office 365 Backup
  • Penetration Testing
  • Security Awareness Training
  • Sentinelone
  • SIEM
  • Vulnerability Management
  • Soc 2 Compliance
  • Business Cyber Security Policies

Useful Links

  • Shop.netlogyxit.com.au
  • Refurbished Hardware
  • Office 365
  • Remote Working Support

Contact Info

  • unit 19b 9-11 Lawrence Drive Nerang Qld 4211
  • sales@netlogyx.com.au
  • 0755201211
© Copyright 2026 Netlogyxit®. All Rights Reserved – Designed by Friendsco Tech.
  • Home
  • About
  • Contact
  • Privacy
  • Terms